So I set up a lot of test machines. A lot. It’s always a pain to load all the basic tools over and over again along with doing all the Microsoft updates and reboots. I found a cool website that expedites the setup of many of the tools I use. Take a quick look at Ninite.com and you won’t be sorry. It basically allows you to select many commonly used applications and download and install them all at once. Very cool and very useful.
Tuesday, February 16, 2010
Friday, February 05, 2010
iptstate – Who you talkin’ to Willis?!?!
I was playing around with iptables today on some new boxen and found an old tool I had forgotten about. iptstate is like top for iptables. It’s a cool tool used to see who is connecting to your linux pc. Here’s an example of the output (with the ip addresses and ports changed to protect the innocent!):
IPTables - State Top
Version: 1.4 Sort: SrcIP s to change sorting
Source Destination Proto State TTL
10.0.10.48:43081 12.18.123.135:7666 tcp TIME_WAIT 0:01:08
10.4.17.49:59253 92.16.123.155:9666 tcp TIME_WAIT 0:00:56
10.23.14.147:1900 15.18.61.105:12 tcp ESTABLISHED 119:59:59
10.6.12.106:1549 213.168.1.105:89 tcp TIME_WAIT 0:00:00
12.34.34.113:42343 121.138.1.103:87 tcp ESTABLISHED 72:35:23
21.15.2.26:3404 107.168.1.102:80 tcp ESTABLISHED 6:56:27
22.16.14.120:3783 145.168.1.120:77 tcp ESTABLISHED 29:13:09
23.154.11.20:2517 123.18.1.100:8080 tcp ESTABLISHED 15:41:32
24.184.14.12:1511 155.168.1.100:34 tcp ESTABLISHED 40:02:34
Enjoy!
Thursday, January 21, 2010
Big A$$ Backups to Removable Media
Ever asked to backup a boatload of files to DVD? Been stymied time after time adding just one too many files to a folder and it won’t fit on DVD/CD? Enter Capacity. A tool to break up that big job into just the right size chunks saving you time and heartache!
Enjoy!

Tuesday, January 19, 2010
You are ready for DNSSEC right?!?!?
If you’ve not heard, time is growing short. A massive rollout of DNSSEC will begin next week. Learn more about it here. I’m sure the change won’t be seamless and it will probably slow name resolution for awhile. Might be a good time to start reading if you haven’t begun already….
Wednesday, January 13, 2010
SELinux Issues
I had a few issues on a CentOS box today that I upgraded from 4 to 5. Syslog wouldn’t start if SELinux was in enforcing mode. I had to do a filesystem-wide relabel to get it all working. It was pretty straight forward to do but here was the procedure that worked for me.
- First make sure SELinux is up to date with a yum update
- Put SELinux into Permissive mode (setenforce 0)
- Now set it so that it won’t turn on after a reboot by editing /etc/selinux/config and setting the line SELINUX=permissive
- reboot (not sure this is required but I did)
- set the system to autorelabel (touch /.autorelabel)
- now reboot again (this one is required and it may take a little while if you’ve got a big filesystem)
- now run setenforce 1 and edit /etc/selinux/config and set it back to SELINUX=enforcing
That was pretty much it. A “service syslog restart” got it all going again.
I’m still learning about SELinux. Here is a great PowerPoint on it.
Enjoy.
Monday, January 04, 2010
Windows 7 GodMode Folder
Happy New Year!
As you can tell I’ve been on vaca for a few weeks so I haven’t posted much. I’ve been reading up on Windows 7 so I’ll be releasing some of what I’ve found over the next few updates. As I this is my first day back to work in two weeks I’ll keep this one simple. You may have seen this around the net already but I thought it was kinda cool. In Windows 7, there is the ability to create a “Control Panel-like” folder that has all the admin stuff that seems awfully hard to find in the new “forced” view of control panel. (I say that because the took the damn classic view of control panel completely out of Windows 7. Damnit.) Anyhow on any drive create a new folder and call it:
GodMode.{ED7BA470-8E54-465E-825C-99712043E01C}
Now when you access that folder the goodies inside let you have a central location to go find a bunch of admin goodies.
Enjoy!
Monday, December 14, 2009
LogMeIn Express
It’s no secret that I love me some LogMein. The simple, free version is excellent and I really depend on it for connecting to a few machines I have out on the Internet. Now they’ve come out with LogMeIn Express which is a no frills screen sharing tool. I’ve played with it a little this morning and I see huge potential for this tool. It offers shared remote control and the ability to send files between people in the meeting. It’s still in beta at this point but let’s hope they release this tool without a price tag. This will even be useful as a replacement for CrossLoop since it’s download component is all browser based. Nice work LogMeIn! Try not to ruin it with a monthly fee!

Thursday, December 03, 2009
GoogleDNS
I've posted before about how much I like OpenDNS. Well it seems that Google wants some of that business now so in early December they created their own public DNS servers. Here's a nice little writeup on it. Is this good news??! Well, as a consumer I'd say yes. For me more is always better. In the past I always used 4.2.2.1 (which I think is Level 3) for DNS and had great luck with it. I know that it uses IP Anycast so it always pulls from a sever geographically close to you. I'm not sure any of the others do that but I can say that I've seen the best name resolution performance from OpenDNS...even when you use their filtering. So now it seems that their is a host of DNS servers to choose from:
Level3 (4.2.2.1 - 4.2.2.6)
Google (8.8.4.4 & 8.8.8.8)
OpenDNS (208.67.222.222 & 208.67.220.220)
DNSAdvantage (156.154.70.1 & 156.154.71.1)
An added benefit of Google's DNS is that it responds to pings and 8.8.8.8 is an easy address to remember. :)
Here's a nice blog post from the founder of OpenDNS on Google's public DNS announcement.
Monday, November 30, 2009
Blackberry Bold 9700
Well I finally upgraded from my 2007 Samsung BlackJack (which I had hacked to Windows Mobile 5.1) to a Blackberry Bold 9700 and I love it. I’ve been very pleased with the phone quality and the trackpad kicks ass. I was always a bit hesitant with Blackberry devices because of the trackball but the trackpad is nothing if it’s not elegant. The phone has pretty much everything I need. 
Friday, November 20, 2009
Windows 7 First Look
I’ve been extremely busy lately with budgeting, reviews and plans for 2010 so I haven’t had as much time to mess with the fun stuff. However, Windows 7 and Office 2007 are in the plans for next years project list. Having been an MCSE since 1995 and having been recertified 3 times as the operating systems change I’ve developed quite a background in Windows. I’ve lived through rollouts of every flavor of Microsoft desktops operating system (except that nasty Vista) by the hundreds. From what I’m reading so far Windows 7 does seem to be a significant upgrade from XP and seems to be well worth the effort. In particular the features that seem most compelling to me are DirectAccess, Problem Steps Recorder, booting from a VHD file, Bitlocker enhancements, integrated Biometric software (thank God…3rd party apps here in XP and Vista have always been painful) and believe it or not….searching in the UI. Searching for files and data has always been weak in Windows (they really need an updatedb & locate equivalent) but from what I’ve seen with search filters Windows 7 looks pretty good. Since they have now removed the Classic interface completely I’ll need to spend some time to find out where they’ve hidden everything. (Damn them.)
We will undoubtedly use MDT 2010 for image development and distribution but I haven’t seen a whole lot of compelling changes in MDT. So far, it looks like they’ve made some work-arounds to the existing pain points but nothing revolutionary. Multicasting will be a nice addition but heck that’s been around for over 10 years in other software distribution products like Ghost anyhow.
I think I’ve decided to move on and get certified as a MCITP: Enterprise Administrator. I don’t believe certifications make you a better engineer, but I do believe the process allows you to take some time to really learn the products and features. This is if you say away from the braindump sites and focus on the learning instead of the testing. I remember back when I got my MCSE 3.51 on NT…It took me 6 months. I read every book I could get my hands on, demo’ed every feature in my lab and worked with the product in my job on a daily basis. That is my plan here as well. The things I learned have stuck with me throughout my IT career and have shaped and molded my ability to understand and consume new technology. I’ll get off my soapbox now…
Stay tuned and I plan to blog about the cool new stuff as I run across it in my studies…
Monday, October 26, 2009
OpenVPN misfire
I spent the weekend testing out OpenVPN-AS and ran into one problem. After an hour or two the connection would die and not restart until I completely exited the software and got back in. Once and awhile I noticed that it would lock out my account. After some mulling around, I figured out that it had something to do with the SecurID authentication. I moved from PAM to RADUIS authentication on Friday in hopes that our users could use their keyfobs and not have to remember a separate username/password combo. Although I got it all working, it seems that there is some kind of reauthentication happening during the session on a frequent basis. I'm guessing there is some kind of a timing issue because everyone once and awhile the attempt fails and the session dies. Moving back to PAM (that's basically Linux authentication against the local databasse) seems to have resolved the issue. Time to get WireShark out and see what's happening. Stay tuned...
Tuesday, October 20, 2009
OpenVPN-AS
Today I set up our first OpenVPN-AS server and man is it cool. A lot of the things I didn’t like about regular OpenVPN (managing certificates, difficult authentication mechanisms, command line management, etc.) are addressed in OpenVPN-AS. You couldn’t ask for better licensing either….$5 per concurrent connection. That’s a software model I can buy into!

First I set up a CentOS server. It’s ver 5.3 with minimal stuff loaded. The I downloaded and ran the rpm right from OpenVPN.net. After a few small configs in pfSense to port forward https over the box I was up and running. I even got RADIUS authentication working of my SecurID box. For testing I just registered for the free 2 user license but I plan on purchasing more after our pilot is complete. If you want VPN for your business the cost is way worth the effort on this package. The difference between configuring OpenVPN and OpenVPN-AS is huge. OpenVPN-AS is way easier to set up and deal with both as an administrator and a user. Now…if they could only include OpenVPN-AS as a package in pfSense…..
Wednesday, October 14, 2009
Super Video conversion
Every once and awhile you hit a cool tool that you’ve seen before but forgotten completely. I ran into Super today while researching video conversion tools and forgot about how useful this tool is. Super is a video conversion program that will let you re-encode video files from one format to another. I even like it better then…choke…sniff…VLC…for some conversions even though it’s not Open Source. :) I ran into this tool a few years ago and it got me out of a tight spot and it’s even better now. What I really like is it’s simplicity. VLC tends to force you to learn all about audio and video codecs if you want to get power out of the tool. Super allows you to pick an “output container” like mpg, wmv, etc. and if does all the hard work picking out the settings for you. It’s great for the video-challenged peeps like me. Enjoy!
Friday, October 09, 2009
pfsense DNS Forwarding and Overrides
I ran into a small DNS issue when I first rolled out our pfsense firewall. I had 4 active interfaces: inside, outside, dmz and wireless. On the PIX I had the wireless segment go directly to the Internet for name resolution. Requests for “inside” services (on the inside or dmz interfaces) were NAT’ed so that the outside public addresses worked correctly. Not wanting to mess with all that NATing again, I was stuck because the rules I wrote were based on private ip addresses which wouldn’t be resolved correctly by a public DNS server. So after messing around a little I found that when set up as a DNS forwarder, the pfsense box will allow you override specific DNS entries or even an entire domain. Very very cool. I simply added the names I wanted to resolve to the override list with their internal ip addresses and bang! The only requirement was DNS forwarding had to be enabled and the pfsense box was acting as the DHCP server on the wireless interface. Simply leave the DNS values empty and pfsense will advertise itself as the DNS server to DHCP clients.
pfsense rocks the house!
Monday, October 05, 2009
Another successful pfsense rollout
This morning, I rolled out pfsense at our biggest site. It was actually the third try, but that’s not pfsense’s fault. A combination of a bad hub and an extremely long arp timeout period on the ISP’s switch scrubbed the first two attempts. (It was really scary to hear the ISP tech say “Sure I can clear the arp cache for you…can you tell me what to type?” Egads!) All in all it went well. One thing I forgot about was access to remote subnets on our WAN. I purposely left them out of the routing table on the firewall thinking I’d use IPSEC tunnels as a failover mechanism to our WAN. Unfortunately, I completely forgot that they get to the DMZ from the inside to see our website. A few quick static routes fixed that in short order.
My biggest surprise was the fact that I disabled bogon login detection on a previous attempt at getting things running so I had to turn that back on. Turns out that doing that will reset the state table and break everyone’s existing connections! Luckily I found that early during the scheduled downtime so no one was the wiser.
Right now I’m backing up the config as I make changes so I need to automate the backup on a scheduled basis like I did with the PIX. I’m sure I can work something out with Cattools for this.
All in all a successful venture. Two more sites to go and all our firewalls will be pfsense!
Tuesday, September 22, 2009
Windows XP Remote Command Line Backup
I had the need today to connect out to a PC and run a backup on it. Turns out this is trivial to do even with the standard windows NTBackup program. From another machine logged in with admin rights to the target machine run the following command:
c:>ntbackup backup \\remotePCnamehere\c$ /j “PC backup name here” /f “c:\backup.bkf”
This will backup the C: drive on the pc named remotePCnamehere locally to your C: in a file called backup.bkf on the box running the command. I can’t believe I haven’t had need for this more often.
Enjoy!
Monday, September 14, 2009
Friday, September 04, 2009
Data Destruction Fun
We often have the need to destroy data on old equipment including hard drives, floppy drives, backup tapes, CD’s, etc. This has always been painful for me because we used to rely on our recycling vendor to assure us that data was being disposed of properly...and I don’t trust anyone. :) For hard drives I like Darik’s Boot-n-Nuke, but it’s a pain to use on loads of removable media. So I went out and bought an Erase-o-Matic 3. 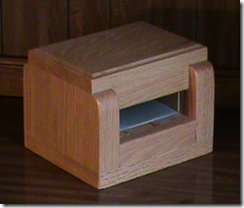
Enjoy the destructive goodness!!!
Friday, August 28, 2009
Technology Conferences
I just returned today from ILTA's 2009 conference in Washington D.C. The conference is always a great opportunity to network and find Legal Technology specific information. This was my fifth year, and although attendance was impacted by the economy the education and networking didn't suffer a bit.
So what take away's did I walk away with? Well there were many. Email management still seems to be a painful topic for most law firms. Time and time again I heard from firms struggling with these issues:
- Lack of firm email retention polices. Conflicting and rapidly changing requirements result in firms talking but doing nothing. Save everything forever ends up being the standard.
- Lack of tools to satisfy the needs of complex policies that require different retention/archival times based upon areas of law, groups of attorneys or specific industry requirements.
- Lack of scalable archival tools. There are some on the market but things like archival indexes and two tiered storage options leave firms wanting more.
- Huge software maintenance costs and low value. Say no more...
- Slow Outlook performance due to "Save everything forever"
- Issues upgrading Exchange because of compatibility issues with plug-in/s for meta data removal, virus scanning, dms integration, encryption, unified messaging, etc....
- Records management as it pertains to email. Even simple point and click tools are too much of a pain for an attorney if he/she can't do it from their berry.
Surprisingly, spam and antivirus weren't huge issues as they once were. Thanks to the development of cloud and appliance based tools you can actually buy your way out of these problems today.
Lots of talk about SharePoint and other portals. Many firms have committed to SharePoint and they pay quite a pretty penny to keep it running and keep specialists on board. Others are frustrated by it's limitations and have developed ways "around" SharePoint. Personally I don't like either answer. Our extranet provider has turned out to be a utter disappointment in regard to flexibility and performance so I'll need to work on this a bit.
Social Networking also was a new topic picking up interest....both in what to do about it and and to use it to your advantage. Although I didn't sit in all the sessions, I didn't hear specific answers to these questions but it was great to toss around the topic with others.
E-discovery raised it's ugly head again (sorry that's just how I feel abouit it) but not too much new in this arena. I'm sure the e-discovery vendors would tell you otherwise but it seemed to me like they are still catching up on features that people need and are still "behind" the curve. Hopefully in the next year or two they will move from reactive to preventative. Isn't it interesting that they spend all their time worry about old data and they don't submit tips on how to keep corporations out of trouble? They already know what not to do but they don't communicate that effectively. It would be a whole new market for them if they looked at what their clients wanted. There was a great reference of this by a speaker one morning showing a picture of a drill. When the CEO of the company asked his employees what it was they said it was what they made... they said they were the world's best power tool supplier (or something like that). Then he had a slide with a picture of a hole in a wall. The CEO told his company that this is what people actually wanted...not the drill. A very insightful observation...
There were many more topics covered and I'll try and write a second edition of this post after I review my notes more. This is just a summary of the topics I found most compelling.
Tuesday, August 18, 2009
ShoreTel Firmware Upgrade and Lessons Learned
So we did an upgrade on our ShoreTel server, switches and phones a few weeks ago and had one small issue. Some (most) of the phones were reporting a “Firmware Version Mismatch” when viewed through ShoreWare Director’s IP Phone Maintenance screen. (To get to this screen go to QuickLook, then pick your site, then pick your switch….about 1/2 way down the screen you see the link to “IP Phones Maintenance”.) The problem ended up being that the DHCP options on the VOIP vlan (192.168.19.x/24) didn’t include the option for the ftp server on the ShoreWare server. 
One other cool thing I learned is that you can telnet into a ShoreTel phone and look at it’s options. To do this you need to use a tool called “phonectl” which is part of the ShoreTel server. Here is how you do it:
From the Shoretel Server directory run the following commands:
1. phonectl -pw <phone password> -telneton <ip address of phone>
2. telnet <ip address of phone>
3. Now, to see the config run “printSysInfo” from the telnet prompt.
Cool.
Subscribe to:
Posts (Atom)


 Posts

